
Sectona at Infosecurity Europe 2025 | June 3–5 | ExCeL London
Stop by our booth (Stand C 95) for live demo of Sectona’s Modern Infrastructure Access Platform
Intelligence System for Monitoring and Assessing

Threat Analytics is a system that enables an organisation to monitor activities of all user sessions, analyse the impounding risks/threats, and take precautionary measures to reduce the impact of an attack going forward. It helps you understand potential risk points or attack surfaces around user activities with the help of Machine Learning algorithms that derive counterintuitive measures to avoid such illegitimate activity.
With the world looking towards a digitalisation era, the stability of business in each and every sector is affected by cyberattacks that are leaving organisations in a vulnerable and impermeable situation.
Hackers are becoming more sophisticated by the day, leading to huge information losses or economic losses. They can be targeting the organisation externally or as an insider irrespective of which it is imperative that we work on mitigating the impounding risk.
Threat Analytics is a system that enables an administrator and an auditor to keep track of all activities in each user session, analysing and working on measures necessary to keep the organisation’s environment safe and secure from any attack.
One of the biggest challenges that often affects threat analytics is disturbances created by false positives generated by security tools and their algorithms.
Threat Analytics needs to be reengineered to identify and discard false positives in order to provide a robust analysis when dealing with large amounts of data.
Privileged Threat Analytics is a more streamlined approach that protects the organisation’s environment from cyber-attacks and insider threats pertaining to privileged account use. It takes information from multiple data points and studies the behaviour of all critical entities in the organisation.
Privileged Threat Analytics analyses the information and aligns itself to detect any kind of malicious activities, abnormal behaviour and analyse any vulnerabilities posed by the existing protocols in the system around focused areas of privilege misuse, privilege abuse, and data theft.
This analysis is put in motion via Machine Learning and Behaviour Analytics processes. It also enables the auditor to track all events and if a malicious activity of critical risk is found, it helps to trace back to the roots of the event to reduce the risk.
Sectona’s Privileged Access Management solution helps avoid threats and discrepancies from any kind of attack vector.
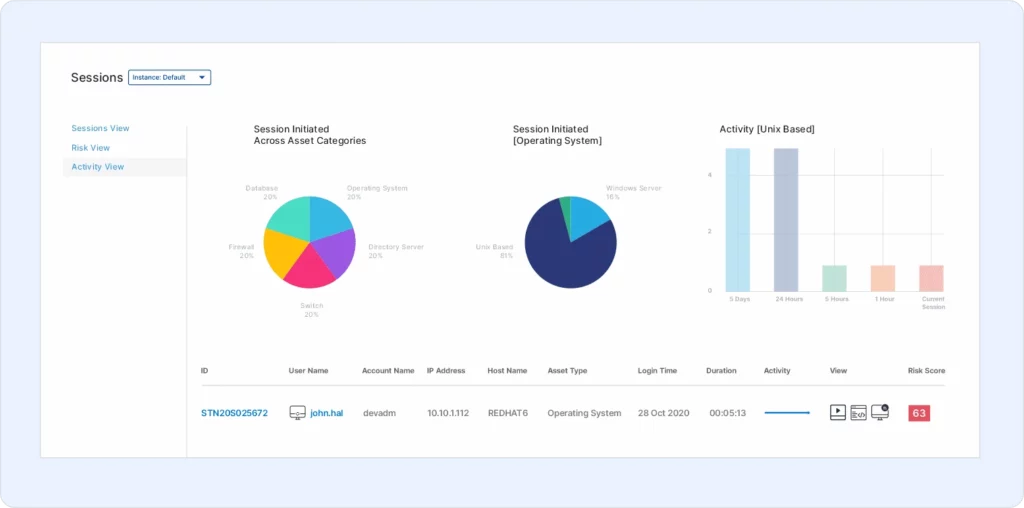
The preview below gives an overview of the activity, the events, and video logs accommodating with the risk score to assess the sessions’ behaviour and threat level.